About ThreatSpire
We built the watchtower we always wanted.
ThreatSpire exists to turn threat intelligence from scattered, unsourced noise into decisions teams can defend. Every adversary tracked, every claim tied to its source, every intelligence requirement answered as the evidence arrives, so security teams spend their time deciding rather than curating. We are building the watchtower for adversary intelligence: always watching, always grounded in proof.
Why we built it
From the trenches, not a whiteboard.
We lived the problem: threat intel that dies in a PDF, claims no one can trace, analysts drowning in feeds while the questions leadership actually asked go unanswered. We have been the people writing those reports at 2 a.m., trying to remember which source said what, and wishing the tool did the curation so we could do the thinking.
Our belief is simple: intelligence is only as good as its evidence. ThreatSpire is opinionated about that. It is evidence-first by construction, MITRE ATT&CK-native, and AI-assisted but always analyst-controlled. We are not building another dashboard. We are building the system we wished we had when the stakes were highest.
The team
Practitioners who have lived the work.
Bob
Co-Founder — CEO
Bob is the co-founder and president of ThreatSpire, bringing nearly a decade of hands-on experience across the full arc of security operations, from the SOC floor to the front lines of incident response and threat intelligence. He built his career the practical way: 24x7 managed security operations triaging alerts for clients across finance, healthcare, retail, and telecommunications, then deeper into the craft as a malware analyst performing static and dynamic analysis of active campaigns. As an incident responder, he developed the playbooks and investigative methodologies that response teams leaned on to scope breaches, gather indicators, and drive escalations. He has worked inside global managed security providers, enterprise security teams, and specialized incident-response consultancies, an unusually complete view of how threats actually get detected, investigated, and stopped. His focus today is threat intelligence: turning raw telemetry, OSINT, and adversary behavior into intelligence that changes what defenders do, rather than intelligence that simply gets read and filed. Making it operational is the whole point. Bob came to security from an unlikely starting point, a degree in criminal justice, and the investigative instinct behind that choice never left him. He still works every threat the way an investigator works a case: follow the evidence, question the assumptions, and do not stop at the surface.
Jason Faulhefer
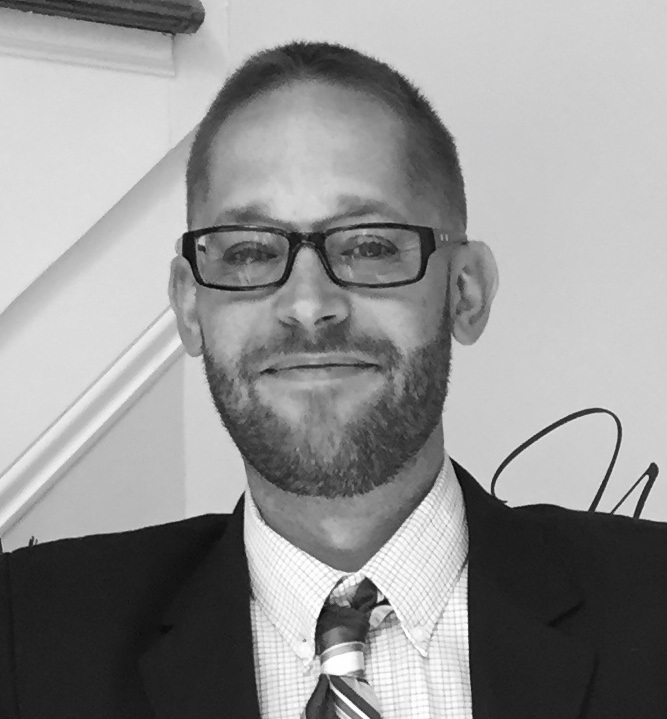
Co-Founder — CTO
Jason brings more than 20 years across offensive security, network and cloud security architecture, and ICS/OT environments. A former U.S. Navy cryptologic technician who served as a wireless ethical hacker on a federal program at the NSA, he has led red teams, penetration testing, and security operations across energy, finance, healthcare, and critical infrastructure. Today he drives ThreatSpire's AI strategy and governance. His career has come down to one thing: finding what others miss and proving it with evidence.
Connect on LinkedInErin Owens
Co-Founder — CISO
Mr. Owens served as a ranking member of the North Texas Crime Commission Cyber Committee and as President of North Texas InfraGard, the FBI's premier cyber outreach partnership. These roles placed him at the center of early national discussions on critical infrastructure protection, intelligence-sharing, and cyber defense strategy.
Throughout the 2000s and early 2010s, Mr. Owens played active roles in shaping multiple regional and national mutual protection initiatives aligned with the National Infrastructure Protection Plan (NIPP) and Presidential Policy Directives 7 and 21. His leadership contributed to the formation or advancement of several key public/private sector partnerships, including:
- Regional Consortium Coordinating Council (RC3)
- RPCFirst
- dfwFIRST
- HoustonFIRST
- Advisory support to multiple Information Sharing and Analysis Centers (ISACs) and Fusion Centers
He also worked directly with Sector Coordinating Councils (SCCs) such as the FSSCC (Financial Services Sector Coordinating Council) and Government Coordinating Councils (GCCs) including the FBIIC (Federal Banking and Insurance Infrastructure Committee).
During the post-Hurricane Katrina recovery period, Mr. Owens helped lead regional efforts to roll out GETS (Government Emergency Telecommunications Service), Wireless Priority Service (WPS), and Telecommunications Service Priority (TSP) for the financial sector across the impacted Gulf Coast region to provide mission-critical government capabilities to the private sector for restoring communications resilience after a national disaster.
These national and regional engagements revealed a persistent, unaddressed gap: while federal and regional initiatives existed, no central coordinating center existed to support private-sector cyber defense preparedness at scale, particularly across critical infrastructure. Recognizing this need, Mr. Owens established the CYBER DEFENSE CENTER, filing it as a Texas nonprofit in 2011 and formally introducing the concept to the RC3 community in 2012.
In 2022, the CYBER DEFENSE CENTER celebrated 10 years of public/private sector collaboration, marking the milestone by opening its research operations to the public. Over the next decade, the Center intends to deliver transformative capabilities, broaden community readiness, and lead the national conversation on wartime and peacetime cyber defense.
What we stand for
Principles that shape the product.
01
Evidence-first
If we cannot source it, we do not assert it. Every claim in ThreatSpire is traceable to its origin — no black-box confidence scores, no unsourced attribution.
02
Analyst-led
AI drafts and accelerates; people decide. We build tools that amplify judgment, not replace it. The analyst is always in control.
03
Built for the work
Shaped by real SOC, CTI, and ICS/OT operations — not a conference room whiteboard. Every feature exists because a practitioner needed it yesterday.
Want to see how we think about intelligence?
See the product in action — built by practitioners, shaped by evidence, ready for your team.